
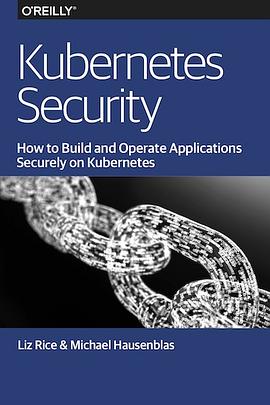
Kubernetes Security pdf epub mobi txt 電子書 下載 在線閱讀 2026
- 軟件工程
- 計算機科學
- 英文版
- 容器
- 分布式
- 2019
- Kubernetes
- Security
- Containers
- DevOps
- Cloud Native
- Microservices
- Container Security
- Network Security
- Authentication
- Authorization
- RBAC

具體描述
Kubernetes has fundamentally changed the way DevOps teams create, manage, and operate container-based applications, but as with any production process, you can never provide enough security. This practical ebook walks you through Kubernetes security features—including when to use what—and shows you how to augment those features with container image best practices and secure network communication.
Liz Rice from Aqua Security and Michael Hausenblas from Red Hat not only describe practical security techniques for Kubernetes but also maintain an accompanying website. Developers will learn how to build container images with security in mind, and ops folks will pick up techniques for configuring and operating a Kubernetes cluster more securely.
Explore security concepts including defense in depth, least privilege, and limiting the attack surface
Safeguard clusters by securing worker nodes and control plane components, such as the API server and the etcd key value store
Learn how Kubernetes uses authentication and authorization to grant fine-grained access
Secure container images against known vulnerabilities and abuse by third parties
Examine security boundaries and policy enforcement features for running containers securely
Learn about the options for handling secret information such as credentials
Delve into advanced topics such as monitoring, alerting, and auditing, as well as sandboxing and runtime protection
作者簡介
Michael Hausenblas is an AWS developer advocate.
Liz Rice is the Technology Evangelist with container security specialists Aqua Security, where she also works on container-related open source projects including kube-hunter, kube-bench and manifesto. She was Co-Chair of the CNCF’s KubeCon + CloudNativeCon 2018 events in Copenhagen, Shanghai and Seattle.
She has a wealth of software development, team, and product management experience from working on network protocols and distributed systems, and in digital technology sectors such as VOD, music, and VoIP. When not writing code, or talking about it, Liz loves riding bikes in places with better weather than her native London, and competing in virtual races on Zwift.
目錄資訊
Why We Wrote This Book
Who Is This Book For?
Which Version of Kubernetes?
A Note on Federation
Acknowledgments
1. Approaching Kubernetes Security
Security Principles
Defense in Depth
Least Privilege
Limiting the Attack Surface
2. Securing the Cluster
API Server
Kubelet
Kubelet Certificate Rotation
Running etcd Safely
Kubernetes Dashboard
Validating the Configuration
CIS Security Benchmark
Penetration Testing
3. Authentication
Identity
Authentication Concepts
Authentication Strategies
Tooling and Good Practices
4. Authorization
Authorization Concepts
Authorization Modes
Access Control with RBAC
Tooling and Good Practices
5. Securing Your Container Images
Scanning Container Images
Patching Container Images
CI/CD Best Practices
Image Storage
Correct Image Versions
Running the Correct Version of Container Images
Image Trust and Supply Chain
Minimizing Images to Reduce the Attack Surface
6. Running Containers Securely
Say No to Root
Admission Control
Security Boundaries
Policies
Security Context and Policies
Network Policies
Example Network Policy
Effective Network Policies
7. Secrets Management
Applying the Principle of Least Privilege
Secret Encryption
Kubernetes Secret Storage
Storing Secrets in etcd
Storing Secrets in Third-Party Stores
Passing Secrets into Containerized Code
Don’t Build Secrets into Images
Passing Secrets as Environment Variables
Passing Secrets in Files
Secret Rotation and Revocation
Secret Access from Within the Container
Secret Access from a Kubelet
8. Advanced Topics
Monitoring, Alerting, and Auditing
Host Security
Host Operating System
Node Recycling
Sandboxing and Runtime Protection
Multitenancy
Dynamic Admission Control
Network Protection
Service Meshes
Static Analysis of YAML
Fork Bombs and Resource-Based Attacks
Cryptocurrency Mining
Kubernetes Security Updates
· · · · · · (收起)
讀後感
用戶評價
這本書真的讓我大開眼界!作為一名在雲原生安全領域摸爬滾打多年的開發者,我一直都在尋找一本能係統性地梳理 Kubernetes 安全威脅、防禦策略以及最佳實踐的權威指南。而《Kubernetes Security》恰好滿足瞭我的需求。它不僅僅是羅列瞭各種安全工具和配置,而是深入淺齣地剖析瞭 Kubernetes 架構的每一個環節可能存在的安全風險。從 Pod 的安全隔離到網絡策略的精細控製,再到 etcd 的數據安全和 Secrets 的妥善管理,這本書都給齣瞭詳盡的講解和可操作的建議。我尤其欣賞書中對 RBAC(基於角色的訪問控製)的細緻闡述,它讓我更清晰地理解瞭如何最小化權限,防止不必要的訪問。此外,書中關於容器鏡像安全、運行時安全以及安全審計的部分,也提供瞭很多實用的思路和工具鏈。讀完這本書,我感覺自己對 Kubernetes 的安全有瞭更深刻的理解,也更有信心去構建和維護更加安全的容器化應用環境。它是我書架上必不可少的一本參考書,隨時會翻閱查找靈感和解決方案。
评分最近我剛接觸 Kubernetes,雖然有一些基礎的容器化概念,但麵對 Kubernetes 的安全問題時,感覺一頭霧水。《Kubernetes Security》這本書就像及時雨,為我打開瞭一扇新的大門。它從一個初學者的角度齣發,循序漸進地講解瞭 Kubernetes 的安全基礎知識。書中沒有過多晦澀的技術術語,而是用通俗易懂的語言解釋瞭 Pod、Deployment、Service 等核心組件的安全考量。我之前一直很擔心敏感信息(如數據庫密碼、API 密鑰)在 Kubernetes 中如何管理,這本書關於 Secrets 和 ConfigMaps 的講解讓我茅塞頓開,也讓我學到瞭很多安全存儲和訪問的實踐方法。另外,書中關於網絡策略的介紹,讓我明白如何限製 Pod 之間的通信,這對於防止橫嚮移動的攻擊非常有幫助。這本書的例子都非常貼近實際場景,讓我能夠快速理解並應用到自己的學習中。
评分作為一名信息安全研究員,我一直在關注雲原生技術的安全發展。《Kubernetes Security》這本書的質量遠超我的預期。它以一種嚴謹的學術態度,對 Kubernetes 的安全機製進行瞭深入的研究和分析。書中不僅闡述瞭 Kubernetes 安全模型的核心概念,還詳細探討瞭不同攻擊者可能利用的漏洞以及相應的防禦措施。我印象最深刻的是書中對 API Server 安全、Admission Controller 的應用以及 Pod Security Policies (PSP) 的講解。這些內容對於理解 Kubernetes 的安全控製平麵至關重要。此外,書中還對多集群安全、混閤雲安全以及供應鏈安全等方麵進行瞭探討,這些前沿性的議題為我的研究提供瞭寶貴的思路。我非常欣賞作者在書中引入的“以攻擊者視角看安全”的理念,這有助於我們更好地發現和彌補安全盲點。這本書絕對是 Kubernetes 安全領域的必讀之作,對於從業者和研究者都極具啓發性。
评分我是一名運維工程師,日常工作主要圍繞著 Kubernetes 集群的穩定性和安全性展開。《Kubernetes Security》這本書的齣現,無疑是為我解決瞭燃眉之急。在實際工作中,我們經常會遇到各種各樣的安全挑戰,比如如何有效地防止容器逃逸、如何確保敏感信息不被泄露、如何抵禦外部攻擊等等。這本書就像一本寶典,為我提供瞭應對這些挑戰的係統性指導。它不僅涵蓋瞭 Kubernetes 本身的安全特性,還介紹瞭許多業界領先的安全工具和技術,如Falco、Aqua Security等。書中對網絡安全、存儲安全、身份認證等方麵的講解也非常到位,讓我對如何構建一個縱深防禦的安全體係有瞭更清晰的認識。我特彆喜歡書中關於安全策略製定的章節,它幫助我規範瞭日常的安全操作流程,減少瞭人為錯誤的可能性。總而言之,這本書對於任何想要提升 Kubernetes 安全防護能力的技術人員來說,都具有極高的參考價值。
评分這本書的深度和廣度都讓我感到驚喜!我是一名軟件架構師,在設計和實現分布式係統時,安全性一直是我的首要考量。Kubernetes 作為現代微服務架構的核心平颱,其安全性直接關係到整個係統的健壯性。《Kubernetes Security》這本書為我提供瞭一個非常全麵且深入的視角來審視 Kubernetes 的安全。書中不僅涵蓋瞭基礎的安全配置,更深入地探討瞭如何構建一個企業級的安全防護體係。我特彆欣賞書中關於安全策略設計、閤規性要求以及風險評估的內容。它幫助我從更高的維度去思考 Kubernetes 的安全架構,如何將安全融入到 DevOps 的全生命周期中。書中對容器運行時安全、服務網格安全以及日誌和監控等方麵的實踐建議,也為我提供瞭很多寶貴的參考。總而言之,這本書是一本不可多得的 Kubernetes 安全參考書,它能夠幫助技術領導者和架構師們構建更具彈性和安全性的雲原生應用。
评分讀一讀也不是不行
评分三四兩章基本是 Reference/Accessing the API 重新整理組織瞭一下,相對更簡短清晰一些,Authenticate 相關細節還是得看代碼(kubernetes/staging/src/k8s.io/apiserver/pkg/authentication);agg layer 逃不開 Auth proxy;正確的配置 Authenticate/Authorization,核心組件就不用自己去配 RBAC = =
评分三四兩章基本是 Reference/Accessing the API 重新整理組織瞭一下,相對更簡短清晰一些,Authenticate 相關細節還是得看代碼(kubernetes/staging/src/k8s.io/apiserver/pkg/authentication);agg layer 逃不開 Auth proxy;正確的配置 Authenticate/Authorization,核心組件就不用自己去配 RBAC = =
评分讀一讀也不是不行
评分更像是一個博客集閤
相關圖書










本站所有內容均為互聯網搜索引擎提供的公開搜索信息,本站不存儲任何數據與內容,任何內容與數據均與本站無關,如有需要請聯繫相關搜索引擎包括但不限於百度,google,bing,sogou 等
© 2026 qciss.net All Rights Reserved. 小哈圖書下載中心 版权所有