
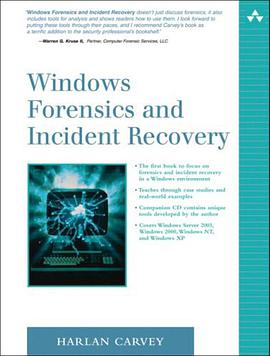
Windows Forensics and Incident Recovery (Addison-Wesley Microsoft Technology Series) pdf epub mobi txt 電子書 下載2026
- Windows Forensics
- Incident Response
- Digital Forensics
- Security
- Windows Security
- Malware Analysis
- Data Recovery
- Investigation
- Computer Forensics
- Addison-Wesley

具體描述
As long as networks of Microsoft Windows systems are managed,administered, and used by people, security incidents will occur. Windowssystems are highly pervasive throughout the entire computing infrastructure,from home and school systems, to high-end e-commerce sites. In contrast tothis pervasiveness, information regarding conducting effective incidentresponse and forensic audit activities on Windows systems is limited. Whilethere are many security books available, none focus specifically on Windowssecurity. There are also resources available online, but they are scattered andoften too general. This book is a compilation of all the information currentlyavailable on this subject. It is for anyone who manages or administers Windowssystems (including home users) and needs to know how to react when theysuspect that an incident has occurred. It guides the reader throughinformation, tools, and techniques that are required to conduct incidentresponse or a live forensics audit activities. By providing the necessarybackground for understanding how incidents occur and how data can behidden on compromised systems, the reader will have a better understanding ofthe "whys" and "hows" of incident response and forensic audit activities. *It isimportant to note that regulatory issues are also pushing organizations towardbetter security and incident preparedness policies.
作者簡介
目錄資訊
讀後感
用戶評價
相關圖書











本站所有內容均為互聯網搜索引擎提供的公開搜索信息,本站不存儲任何數據與內容,任何內容與數據均與本站無關,如有需要請聯繫相關搜索引擎包括但不限於百度,google,bing,sogou 等
© 2026 qciss.net All Rights Reserved. 小哈圖書下載中心 版权所有